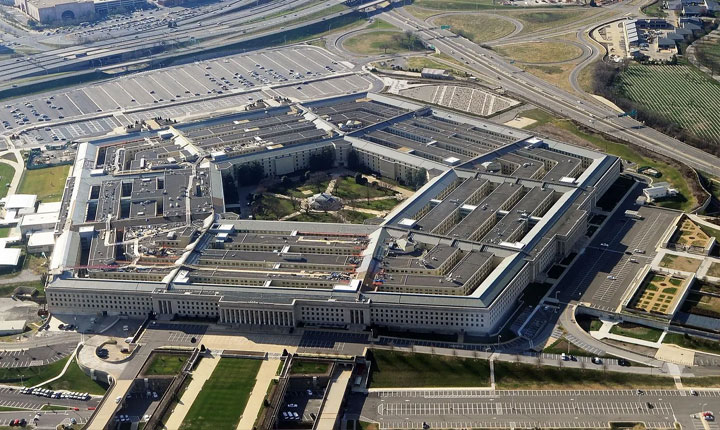


A major cyber security breach has hit the United States Department of Defense, compromising an information system managed by the Defense Manpower Data Center (DMDC). Unauthorized users managed to infiltrate the system and remain undetected for approximately nine months, from October 2025 until July 2026. The incident exposed sensitive personal details belonging to nearly 3.05 million individuals comprising 2.76 million living persons and 294,000 deceased records. The compromised information includes full names, Social Security numbers (SSNs), dates of birth, contact details, and specific military occupational data.
Vulnerabilities and Lack of Encryption:
A critical factor that heightened the severity of the incident was that vital personal information was left unencrypted, making it easily readable. Upon discovering the flaw, Pentagon officials immediately patched the vulnerability, restored the system, and initiated incident-response protocols. While authorities report no current evidence indicating that the stolen data has been maliciously exploited or misused, affected individuals are being provided with one year of complimentary credit monitoring and identity protection services.
Implications for National Security:
The DMDC serves as a central repository for the Department of Defense, overseeing over 60 million records that encompass active-duty service members, reservists, civilian employees, contractors, retirees, veterans, and their family members. Security experts warn that the exposure of detailed job titles and ranks alongside social security numbers poses a substantial strategic risk, potentially allowing hostile actors to analyze military structures. This breach occurring alongside a separate security scare on an FBI job portal involving a threat group named “Shiniganhers” has sparked serious concerns regarding the digital defense readiness and infrastructure vulnerabilities of key U.S. government agencies.